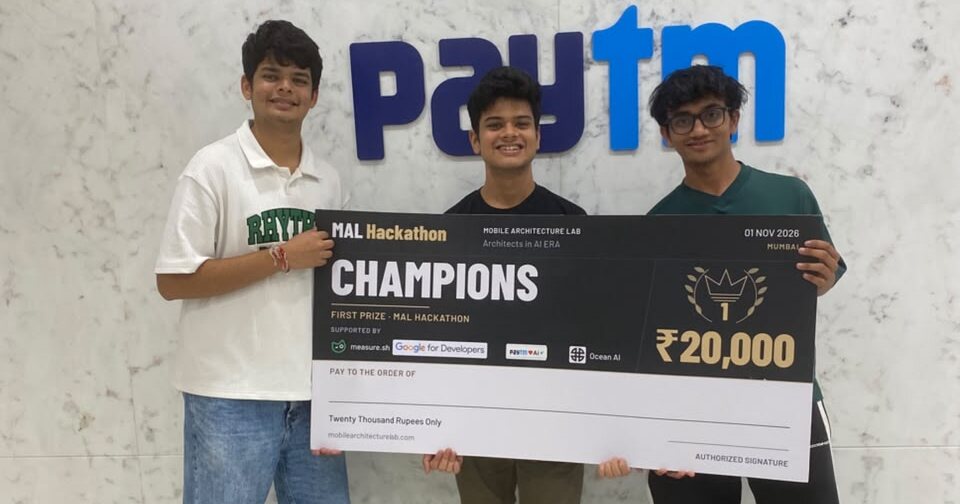
Clinic booking system design: PostgreSQL locks and ADRs at MAL 4
How our three-person team designed a clinic appointment prototype at MAL 4 using PostgreSQL row locks, a partial unique index, idempotency keys and 19 ADRs.
All posts
Self-hosting college infrastructure with Coolify, Mailcow and Discord
How I run ACM MPSTME's self-hosted infrastructure: Coolify deployments, Mailcow email for 7–9 committees, member mailboxes and Discord-based access.
AI vulnerability variant analysis: VARSEER benchmark results and limits
My VARSEER study compares clone matching, retrieval signals and LLM triage on 49 vulnerability families across 12 C projects, including negative results and uncertainty.
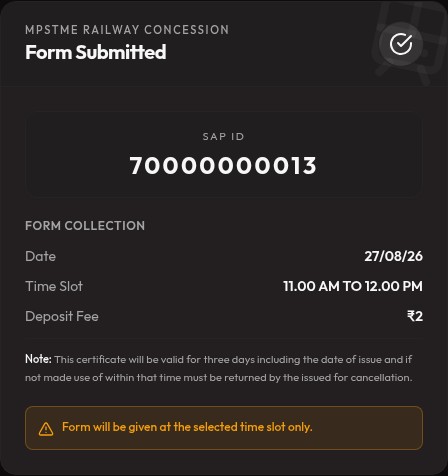
Maintaining a student portal: booking rules, PostgreSQL and admin workflows
How I maintain MPSTME's railway-concession portal for approximately 4,000 students: server-side booking rules, PostgreSQL history, admin tools and daily email reports.
Building a QR check-in system: PostgreSQL race conditions and role-based access
How I built Social Conclave's QR check-in system for 500+ delegates, with editable role permissions, manual scanning fallback and PostgreSQL duplicate prevention.
End-to-end encrypted file sharing: GhostShare's browser encryption design
How I designed GhostShare's encrypted notes and file sharing with browser-side Argon2id, AES-256-GCM, direct uploads to Cloudflare R2 and explicit trust limits.
Building a database storage engine in Java: B-Trees, tombstones and compaction
How I built bad-db, a Java storage engine with a binary record format, an in-memory B-Tree index, tombstone deletes and compaction, and what it lacks for durability.
LLM prompt injection: lessons from building a jailbreak contest
What running Fool The LLM taught me about prompt injection, encoded secret leaks, streaming-output checks and authorization outside the language model.